Shadow AI Risk: Why Unsanctioned AI Tools Are Your Biggest Cybersecurity Threat
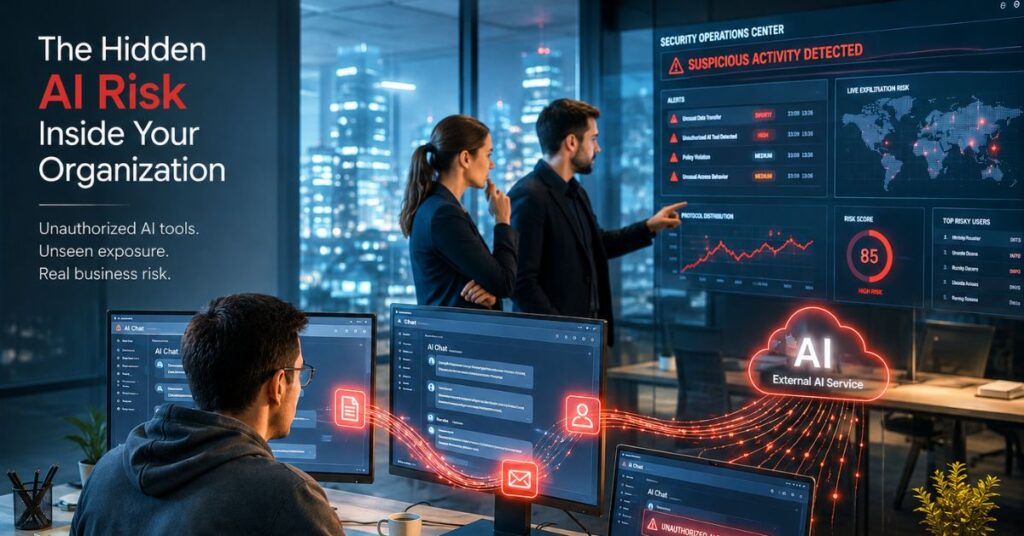
Shadow AI risk is the security, compliance, and operational exposure that occurs when employees use AI tools inside your organization without IT approval, security review, or governance oversight.
Unsanctioned AI tools, such as ChatGPT, free writing assistants, AI browser extensions, and unapproved coding tools, are already running inside most organizations’ daily workflows, and the security teams responsible for protecting that data have no visibility into it.
The result is sensitive data leaving your security perimeter, compliance violations accumulating silently, and an attack surface expanding through everyday conversations that no DLP rule was ever built to catch.
What Is Shadow AI Risk?
Shadow AI is the unauthorized, undocumented use of AI-powered tools, apps, or models inside your organization without IT knowledge, security review, or any governance in place. Shadow AI risk is what unauthorized use actually costs you: data leaving your security perimeter, compliance obligations triggered, and your attack surface growing in ways no alert will catch.
Here’s what makes it different from every other security risk you manage. Traditional risks involve data moving to places it shouldn’t be. Shadow AI involves data being processed by systems that can learn from it, retain it, and reproduce it in ways you’ll never be able to trace or reverse. When an employee pastes a proprietary document into a public AI chatbot, there’s no “undo.” That data can influence future model outputs for users who have nothing to do with your organization.
By 2026, this is not a large-enterprise-only problem. According to CISA’s AI risk management guidance, organizations of every size face measurable exposure when AI adoption outpaces governance, and right now, it almost always does.
Shadow AI vs. Shadow IT: A Critical Difference
Most security teams already know how to handle shadow IT, the unauthorized apps, personal cloud storage, and unmanaged devices that appear outside IT’s visibility. The risk is data location. You find the tool, you pull the data, you close the gap. It’s recoverable. Shadow AI doesn’t work that way.
Your sales rep saves a client contract to their personal Dropbox, you can request deletion and move on. That same rep pastes the contract into an AI chatbot to generate a proposal draft more quickly, and you have no way to retrieve anything. The data was processed by an external model under terms your legal team never read. It may have influenced training. There’s no server to call, no file to delete.
Shadow AI also spreads far wider than shadow IT did. It’s not just developers or technically confident employees; it’s HR managers reviewing resumes, finance teams cleaning up decks, and customer support agents drafting faster replies. Anyone with a browser and a deadline is a potential exposure point. That makes this a fundamentally different problem, one that requires its own response.
Why the Spread of Shadow AI Is Accelerating
The honest reason shadow AI keeps growing is that the tools are easier to access than anything IT can provision. No purchase order, no security review, no onboarding session. A free account takes 90 seconds. An internal software approval can take 90 days.
Employees aren’t trying to create security incidents. They’re trying to meet deadlines. When the approved tool catalog is empty and the review queue is backed up, the decision about which AI tool to use is made by whoever needs to send the report by 5 pm.
Three patterns keep reinforcing the problem:
Procurement friction does the recruiting for unauthorized tools
Slow internal approval processes don’t stop AI adoption; they just push it into tools IT doesn’t know about. The bottleneck creates the shadow.
When leadership uses unapproved AI tools, the policy loses credibility
Research consistently shows that unauthorized use of AI tools isn’t confined to junior employees. When executives openly use tools that have not undergone a security review, the message to the rest of the organization is clear.
AI technology evolves faster than any governance framework can keep up with
NIST CSF, ISO 27001, and CIS Controls provide organizations with a strong security baseline, but none were designed with AI-specific data flows or model training dynamics in mind. Most organizations are managing a 2025 AI problem with 2019 governance tools.
The numbers aren’t soft. IDC’s 2025 survey found 56% of employees use unauthorized AI tools at work. Only 23% use AI tools that their organization actually governs. Gartner projects that by 2027, 75% of employees will regularly use apps outside IT visibility, up from 41% in 2022. Security estimates that roughly 90% of enterprise AI usage currently occurs without the knowledge of the security or IT team. That’s not a fringe problem. That’s the baseline.
Shadow AI Examples: What It Looks Like Across Your Organization
Shadow AI is almost never deliberate sabotage. It’s a capable person using a trusted tool to get something done faster. That’s exactly why blanket policies struggle to contain it, you’re fighting human problem-solving instinct, not bad intent.
Here’s what it looks like by role:
A developer debugging a production issue at midnight pastes the relevant code into an AI chatbot. That code might contain API keys, internal architecture details, or logic for an unreleased product. It’s now processed by a model with retention policies the developer has never read.
A finance analyst feeds internal revenue projections into an AI writing tool to sharpen a board deck. The financial strategy your executive team spent weeks building now sits on third-party servers under terms your legal team didn’t approve.
The HR manager uses a free AI screening platform to quickly sort through a high volume of resumes. Candidate PII, names, salary history, and contact details are processed outside any data processing agreement, creating live GDPR and CCPA exposure.
The marketing team inputs competitive intelligence summaries into an unapproved AI platform to generate campaign copy faster. Trade secrets move through a conversational interface that doesn’t register a single DLP alert.
Customer support agent pastes client account details into ChatGPT to draft a more personalized response. Customer PII is now on servers your organization has no contract with and no visibility into.
Not one of these people set out to cause a security incident. Every one of them did.
The Six Security Risks of Shadow AI
Shadow AI creates a category of security and compliance exposure that traditional tools weren’t designed to detect. Each risk below compounds the others.
1. Unauthorized Data Exposure to External AI Models
Every prompt sent to a third-party AI is data leaving your environment. Without vetting the tool, you have no visibility into where that data is stored, how long it’s retained, which jurisdiction it falls under, or whether it feeds future training runs. The Varonis State of Data Security Report found that 99% of organizations have sensitive data exposed to AI tools, a figure that shows how quickly shadow AI went from exception to the norm.
For organizations operating under HIPAA compliance requirements, the exposure is immediate. The moment protected health information touches an unsanctioned system, it’s a compliance violation, not a risk of one.
2. An Attack Surface That Expands Through Conversation
Data entering unsecured AI APIs doesn’t sit dormant; it becomes usable intelligence. Threat actors can use shadow AI-sourced information to build targeted phishing campaigns, deepfake attacks, and social engineering schemes that carry insider-level accuracy. What makes this attack surface particularly dangerous is that it’s invisible. The exposure travels through a chat interface, not a file transfer, so your existing monitoring tools won’t catch it happening.
Most organizations are still running security stacks built around perimeter defense and known malware signatures tools that were never designed to detect data leaving through a browser-based conversation. Understanding the difference between EDR, MDR, and XDR matters in this context, because the coverage gap that shadow AI exploits is exactly what more advanced detection and response layers are built to close.
Learn the difference between EDR vs Antivirus.
3. AI Model Poisoning and Outputs You Can’t Trust
Not every AI tool your employees are reaching for is accurate, vetted, or built with security in mind. Some are trained on biased, low-quality, or deliberately manipulated data. When employees pull AI-generated outputs into official documents or business decisions without verification, that unreliable information enters your workflows with no audit trail. You won’t know which model produced what, or what data influenced it.
4. Compliance Violations That Hit Multiple Frameworks at Once
This is where shadow AI risk gets expensive fast. A single employee interaction involving PII, protected health information, or financial records can trigger simultaneous obligations under GDPR, HIPAA, CCPA/CPRA, PCI DSS, and the EU AI Act. Your compliance team cannot audit what they have no visibility into, and regulatory exposure quietly stacks up in the background.
IBM’s 2025 Cost of a Data Breach Report found that breaches involving shadow AI cost organizations an average of $670,000 more than standard incidents. At the time of breach, 97% of affected organizations lacked proper AI access controls.
5. Intellectual Property Loss You Can’t Walk Back
Source code, patent applications, product roadmaps, and competitive strategy documents pasted into public AI models can become permanently embedded in training datasets. Unlike a document sent to the wrong email, where you can send a retraction and document the remediation, data processed by an AI model isn’t retrievable. The moment the prompt is submitted, the exposure is done. There’s no recovery path.
6. No Audit Trail Means No Incident Response
Shadow AI leaves no log. There’s no record of what data went into which model, what output was returned, or what decisions your team made based on it. When an incident surfaces, and statistically, one will, your incident response process and your compliance reporting both depend on answers that simply don’t exist.
Shadow AI and Compliance: The Frameworks Haven’t Caught Up Yet
The regulatory exposure from unmanaged AI tool usage is specific, growing, and already in effect. NIST CSF, ISO 27001, and CIS Controls provide organizations with a strong security foundation, but none were designed around AI-specific data flows or the model-training dynamics that make shadow AI a distinct risk category.
Here’s where the gaps show up in the frameworks most organizations already operate under:
GDPR Article 28 requires documented data processing agreements with every processor handling personal data. An unsanctioned AI tool has no such agreement. The moment an employee pastes a customer’s name and email into a public chatbot, your organization is in violation, intent is irrelevant.
HIPAA (45 CFR §164.312(b)) requires audit controls that track and log PHI access. If employees are feeding patient data into unvetted AI tools, that requirement becomes structurally impossible to satisfy.
The EU AI Act introduces AI-specific obligations on transparency, data governance, and prohibited use cases. Shadow AI usage can generate liability that organizations don’t even know they’ve taken on, because the tool was never disclosed to legal or compliance.
PCI DSS Requirement 10 mandates logging of all access to cardholder data environments. If cardholder data travels through an unsanctioned AI tool, the logging requirement fails immediately and silently.
In addition to breach costs, GDPR fines can reach up to 4% of annual global turnover. HIPAA penalties run from $137 to $2.067 million per violation category per year.
If your current cybersecurity risk management program doesn’t specifically address AI tool usage, you have a compliance gap, and auditors will find it before your team does.
How to Detect Shadow AI: Six Signals Worth Monitoring

Shadow AI in the workplace: when convenience meets unseen cybersecurity risk.
Shadow AI doesn’t surface through dramatic events. It builds over weeks and months inside normal workflows until a security audit or a breach forces the conversation. Most of these signals are visible with tools your organization already runs.
- Unusual outbound traffic patterns: Repeated HTTPS connections to AI service domains (api.openai.com, claude.ai, gemini.google.com, api.anthropic.com) that don’t appear in your approved software inventory are one of the clearest indicators available.
- Copy-paste behavior on endpoints: Large blocks of text copied from internal applications and pasted into browser tabs is a behavioral signature that’s consistent with employees feeding internal documents into AI chatbots. Endpoint security tools can surface this pattern if you know how to look for it.
- Corporate email addresses registered on AI platforms: Routine credential monitoring picks up when employees sign up for AI tools using their work email. That creates both a data exposure risk and a credential management gap.
- Productivity spikes without an explanation: A team producing deliverables at a pace well above their historical norm, without new headcount or documented tooling changes, warrants investigation. It doesn’t always mean shadow AI, but shadow AI consistently shows up in that pattern.
- Browser extensions for AI-adjacent tools: Grammar assistants, summarization tools, and writing extensions frequently contain embedded AI models that process content on external servers. Every one of these is a potential data channel outside your visibility.
- Qualitative gaps in your software inventory: Exit interviews, engagement surveys, and informal team conversations regularly surface AI tools that never appeared in any IT request. That gap between what IT has provisioned and what teams actually use is often visible in people data before it shows up in technical logs.
One critical limitation to understand: traditional DLP and CASB tools miss most shadow AI activity. They were designed for structured data patterns and file transfers. An employee describing your Q3 financial results to an AI chatbot in plain conversational English won’t trigger a DLP rule, even though the exposure is identical to sending that data in a spreadsheet.
Endpoint security tools that go beyond signature-based detection are better positioned to surface these behavioral patterns. Endpoint protection solutions that monitor process behavior, network calls, and clipboard activity give security teams the visibility that traditional DLP simply doesn’t provide, and for shadow AI specifically, that behavioral layer is often the only way to see what’s moving where.
How to Govern Shadow AI Risk: What Actually Works
Banning AI tools without providing alternatives doesn’t reduce shadow AI, it just makes it less visible. Every organization that has tried this approach reports the same outcome: employees keep using the tools, and the usage just becomes harder to find. Effective shadow AI governance is about structured enablement, not restriction.
Visibility before anything else
You cannot govern what you cannot see. Before writing policies or blocking domains, map which AI tools are actually in use, which teams use them, and what data types are moving through them. Automate that discovery across endpoints, browsers, and SaaS integrations. The picture is almost always worse than IT expects.
An AI acceptable use policy that people will actually read
The policy needs to answer three questions clearly: which AI tools are approved, which data types can never enter any AI system under any circumstances, and how employees request approval for new tools, with a defined turnaround time. Policies that run to dozens of pages don’t change behavior. Short, specific, and actionable.
Sanctioned AI alternatives that close the gap
The single most effective way to reduce unauthorized adoption of AI tools is to provide approved alternatives that actually meet employees’ workflows. Text generation, code assistance, data summarization, and content drafting. Identify your highest-demand use cases before rolling out alternatives, and ensure the tools you provision align with how teams actually work.
Training that explains the why, not just the rule
A customer service agent and a developer face completely different shadow AI risks, and they need to understand that in concrete terms. Role-specific training that shows what data exposure actually looks like in their day-to-day context changes behavior in ways that generic policy reminders don’t. As part of your cybersecurity awareness program, this needs to be ongoing; AI capabilities and risks change fast enough that annual training is already out of date.
Quarterly audits, not annual ones
SaaS vendors quietly and regularly add AI features, often without change notifications. A tool your security team approved and cleared six months ago may now, by default, route data to an external model. Quarterly reviews of network traffic patterns, approved tool capabilities, and team usage habits are the minimum cadence needed to stay current.
As a structured governance framework, the NIST AI Risk Management Framework lays out four functions: Govern, Map, Measure, and Manage, designed specifically for AI-related risks that traditional IT governance doesn’t address.
Frequently Asked Questions
What are the risks of shadow AI?
Shadow AI risks include unauthorized data exposure to third-party models, compliance violations under the GDPR, HIPAA, and the EU AI Act, intellectual property loss, and a lack of audit trail for AI interactions. IBM’s 2025 Cost of a Data Breach Report found that shadow AI-related breaches cost organizations an average of $670,000 more than standard incidents.
What is the difference between shadow AI and shadow IT?
Shadow IT involves unauthorized apps and cloud services, the risk is data location, and exposure is usually recoverable. Shadow AI is different because AI models can learn from, retain, and reproduce sensitive inputs in ways that are difficult or impossible to reverse, making the exposure far harder to contain.
How can organizations detect shadow AI?
Monitor outbound network traffic for connections to known AI domains, check endpoint telemetry for unusual copy-paste patterns from internal apps to browsers, and audit browser extensions for embedded AI features. Traditional DLP tools often miss shadow AI because they’re designed for file transfers, not natural-language chat interfaces.
What is an AI acceptable use policy?
A formal document that defines which AI tools are approved, which data types may never enter any AI system, and how employees request access to new tools, with defined review timelines. It should be short enough to be read and specific enough to guide real decisions.
What are examples of shadow AI in the workplace?
Developers pasting source code into public AI chatbots, finance teams uploading revenue projections into unapproved writing tools, HR managers using free AI to screen resumes, and customer support agents feeding client details into ChatGPT to speed up responses.
How much does shadow AI cost organizations?
IBM’s 2025 Cost of a Data Breach Report puts the additional cost at an average of $670,000 per incident. GDPR fines can reach 4% of annual global turnover, and HIPAA penalties can reach $2.067 million per violation category per year.
What Your Security Team Should Do Next
Shadow AI risk is active, it’s growing, and it’s almost certainly already running inside your organization. The combination of unauthorized data exposure, simultaneous compliance violations across multiple frameworks, and an attack surface that expands through everyday conversations rather than obvious file transfers puts it at the top of the threat list for security teams in 2025 and 2026.
The organizations managing it well are not the ones with the strictest AI bans. They’re the ones who got visibility first, gave employees better-approved options, and built a governance process fast enough to keep pace with how quickly AI adoption actually moves.
If you’re not sure where your organization stands on shadow AI exposure right now, CyberMark Agency helps small and mid-sized businesses build practical AI governance frameworks, along with endpoint protection, compliance reporting, and continuous security monitoring, without the complexity or cost of enterprise security programs. Start with a no-obligation security assessment.
Need help reducing your business security risk?
Contact us

